Cyberattacks Expose Economic Risks in Ukraine and Russia’s Alert Systems
False nuclear, radiation and chemical warnings highlight the growing economic cost of protecting essential public communications infrastructure.
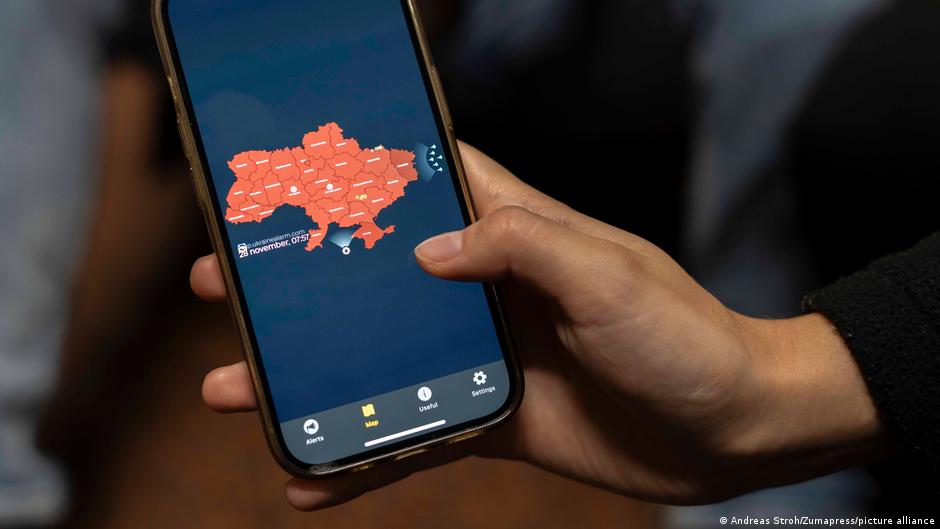
Cyberattacks on government-linked emergency notification services in Ukraine and Russia sent false warnings to users about radiation, chemical hazards, street fighting and nuclear warheads, exposing the vulnerability of digital systems that have become part of both countries’ critical public infrastructure.
Ukraine’s official Air Raid Alert application, which is used to notify the public about threats, came under attack on the evening of Sunday, November 1. Users received fabricated alerts about radiation and chemical dangers, as well as messages warning of possible street fighting in Kyiv.
The Ukrainian Air Force was among the first institutions to respond. It said the application had probably been subjected to “hostile interference” and stressed that there was “no radiation threat.” The State Emergency Service of Ukraine separately said the nationwide warning system was operating normally. According to the agency, genuine threat signals continued to be transmitted to regional administrations and outdoor public-warning systems.
The distinction is economically significant. Digital applications can broaden the reach and speed of emergency communications, but reliance on a single consumer-facing channel can create concentrated operational risk. Maintaining parallel systems—including regional administrative networks and street alerts—adds expense and complexity, yet the incident demonstrated the value of redundancy when one part of the communications chain is compromised.
Trust becomes an economic asset
The developers later confirmed that the application had been breached. “Today, unauthorized third parties interfered with the operation of the application. We disabled push notifications and temporarily suspended the application,” the team said on Telegram. Users were also urged not to follow links contained in suspicious notifications.
That warning points to a wider structural consequence of attacks on public alert services: the immediate technical disruption may be only one part of the damage. Emergency systems depend on users responding quickly and treating notifications as credible. False alarms can weaken that confidence, while suspicious links can introduce additional risks for individual devices and wider digital networks.
Emergency communications carry economic value because their effectiveness depends on speed, reach and public confidence—not merely on whether the underlying software remains online.
During the night of November 2, the Ukrainian development team reported that the service was being restored gradually after the cyberattack. Users again began receiving air-raid notifications, although some functions remained temporarily unavailable. The developers also said the application does not store users’ personal data and that additional cybersecurity protections were being introduced.
The absence of stored personal data, as described by the team, limits one category of potential exposure. It does not, however, eliminate the operational challenge created when attackers gain the ability to distribute false information through a trusted channel. For governments and developers, the episode raises questions about how spending should be divided among prevention, rapid shutdown procedures, backup communications and the restoration of service after an intrusion.
Parallel attack reported in Russia
Russia’s Emergency Situations Ministry reported a hacking incident at almost the same time. The ministry said its mobile application had been subjected to a “massive cyberattack.” According to the agency, attackers used the service to circulate false claims that nuclear warheads had supposedly been launched toward Russia.
The ministry said specialists were working to eliminate the vulnerability and restore the service to normal operation. As in Ukraine, the attack targeted more than software availability: it exploited the authority associated with an official emergency platform to give fabricated information the appearance of legitimacy.
The near-simultaneous incidents illustrate how civilian warning applications have become economically important infrastructure. They sit at the intersection of telecommunications, public administration and national security, serving users at moments when delays or confusion can have serious consequences. Their protection therefore requires more than conventional maintenance. It also demands continuous monitoring, clear institutional coordination and alternative channels capable of carrying verified alerts when an application is disabled.
Historically, public-warning infrastructure has been designed around multiple layers, with central authorities passing information through regional bodies and physical sirens. Mobile applications extend that architecture by placing notifications directly on personal devices. The trade-off is that greater convenience and reach also create a digital point of attack that can be used to generate fear at scale.
For both countries, the longer-term cost will include not only technical repairs but also stronger defenses and efforts to preserve public confidence. The Ukrainian developers’ decision to halt push notifications, restore functions gradually and add protective measures shows how continuity planning becomes central after a breach. The Russian ministry’s work to close the reported vulnerability reflects the same operational pressure.
The attacks ultimately demonstrate that resilience has a recurring price. Governments must fund overlapping warning channels even when they appear inefficient during normal periods, while application operators must prepare to authenticate messages, isolate compromised functions and communicate quickly with users. In emergency infrastructure, redundancy is less a duplication of spending than insurance against the much larger social and economic costs of misinformation during a crisis.